One platform under all three tools
Identity, access, audit and links are built once and shared, so Minerva, Caelus and Mercury behave the same way.
Identity
Sign in through any OIDC provider, such as Microsoft Entra ID, Okta, Google Workspace, Auth0 or Keycloak.
- Users are keyed on a persistent identity, not an email address, so a changed email does not create a new person
- Your identity provider is the source of truth for who people are and which groups they belong to
- Account recovery stays with the identity provider; Castra never handles passwords
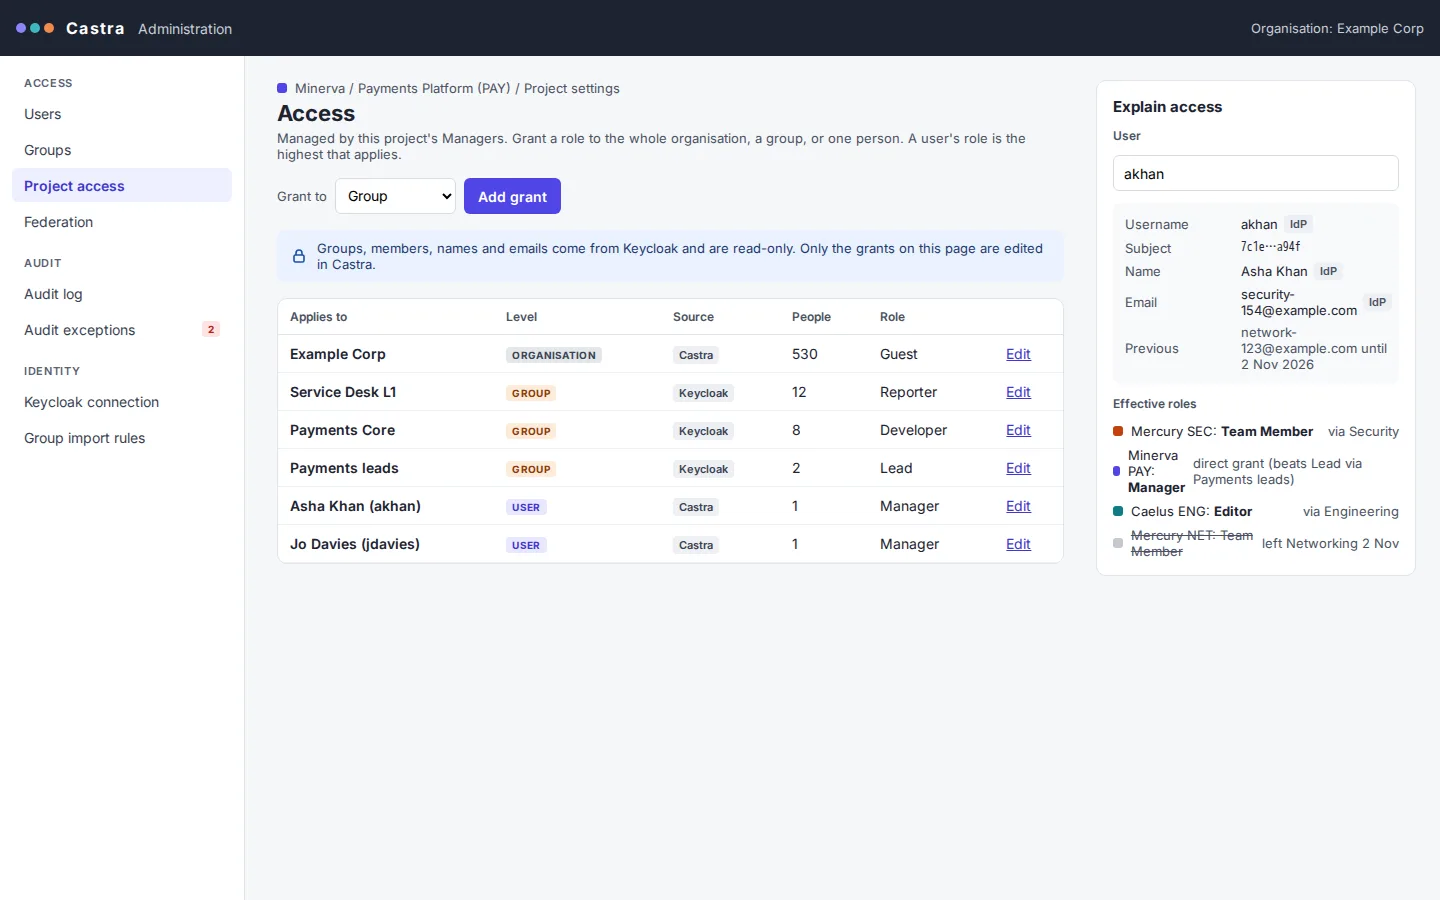
Access, in three levels
Access is set at the level that fits, from the whole installation down to one project.
- PlatformThe installation as a whole.
- OrganisationA tenant of the platform, such as a company or department.
- ProjectWhere the day-to-day work happens.
Project admins map directory groups to roles. A grant can go to the whole organisation, to a directory group, or to one person. Because the identity provider is the source of truth, removing someone from a group removes the access that came with it.
Audit log
Activity across all three tools is written to one tamper-evident log, including exceptions such as a guessed ticket reference.
Smart links
Paste a link to an issue, page or ticket in any tool and it turns into a live preview, subject to what the reader is allowed to see.
Federation
Organisations stay separate by default. Controlled cross-organisation federation lets two of them share what they choose to.