Security by design, in the open
These are design rules, not certifications. Castra is early software and has not been independently audited.
Tenancy isolation
Data is separated by organisation using row-level isolation in the database, so one tenant's queries cannot return another's rows.
Identity
Sign-in goes through your OIDC provider. Users are keyed on a persistent identity, and Castra never handles passwords.
Audit
A tamper-evident log records activity, including attempts that break the visibility rules.
Example: two teams, one problem
Bob is on the network team. He has a ticket on a closed network, and it relates to a DNS ticket owned by another team.
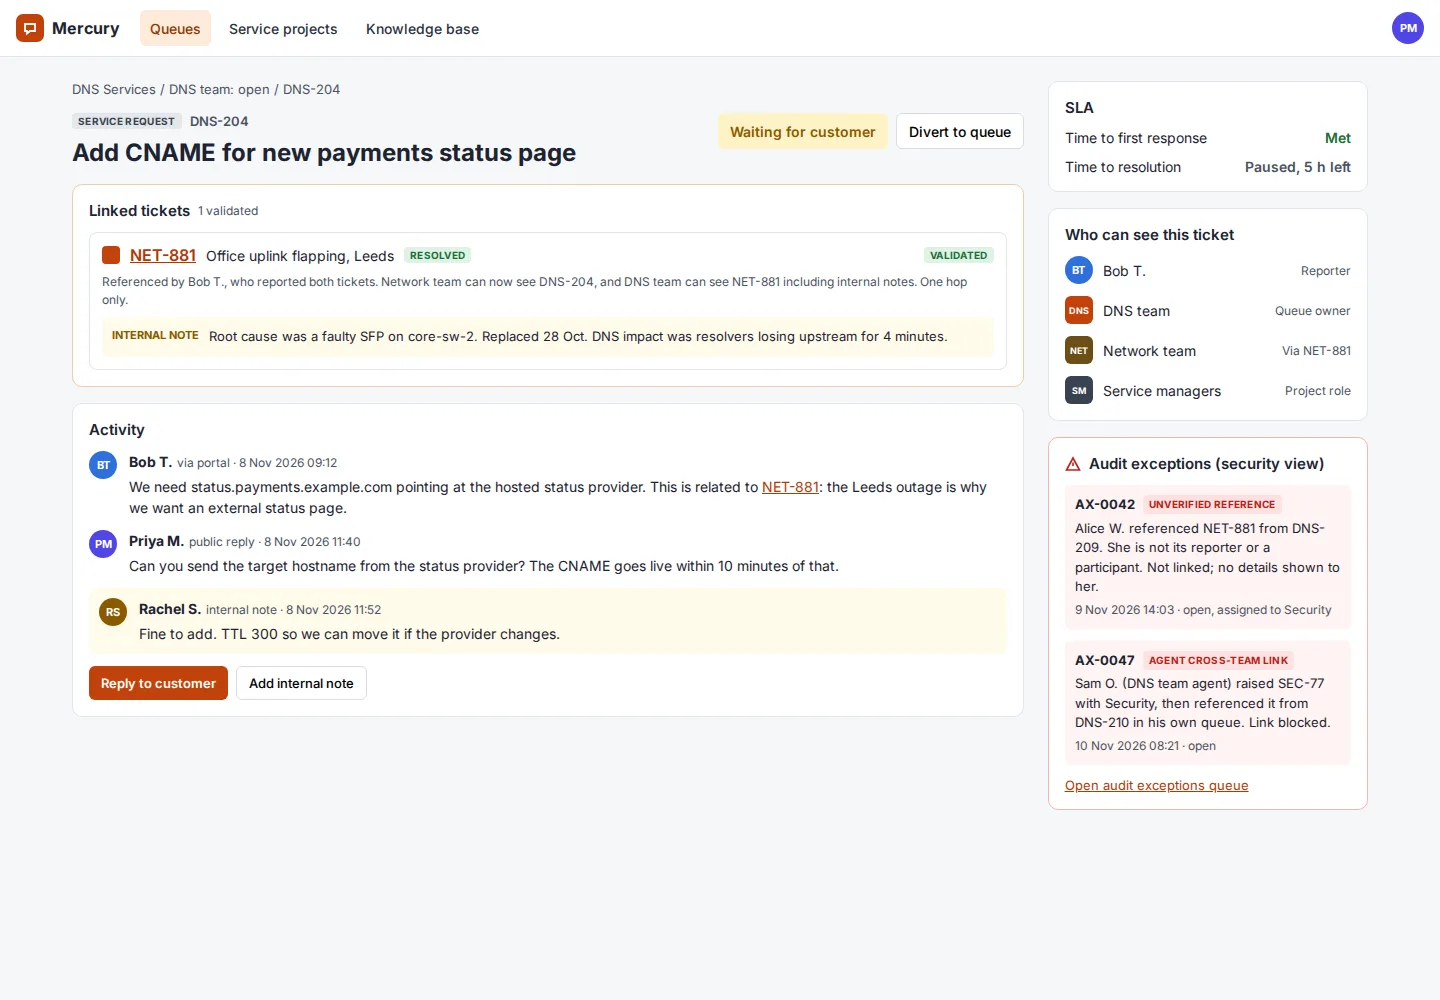
Bob links his ticket to the DNS ticket. Because Bob can validly see both, the link is made, and both teams now see both tickets.
Alice guesses Bob's ticket number. She is not on his team and has no valid link. No link is created, nothing about the ticket is revealed, and an audit exception is raised.
Agents see their team's queues, tickets assigned to them and tickets the requester validly linked. A guessed reference is never enough.
Your data, your boundary
Self-hosted Castra has no telemetry and no licence server, so nothing needs to leave your network. To report a security concern, get in touch.